Looking for On-Demand Tech Support?
Techmate has the boots-on-the-ground IT Support where and when you need it.
Schedule a Discovery Call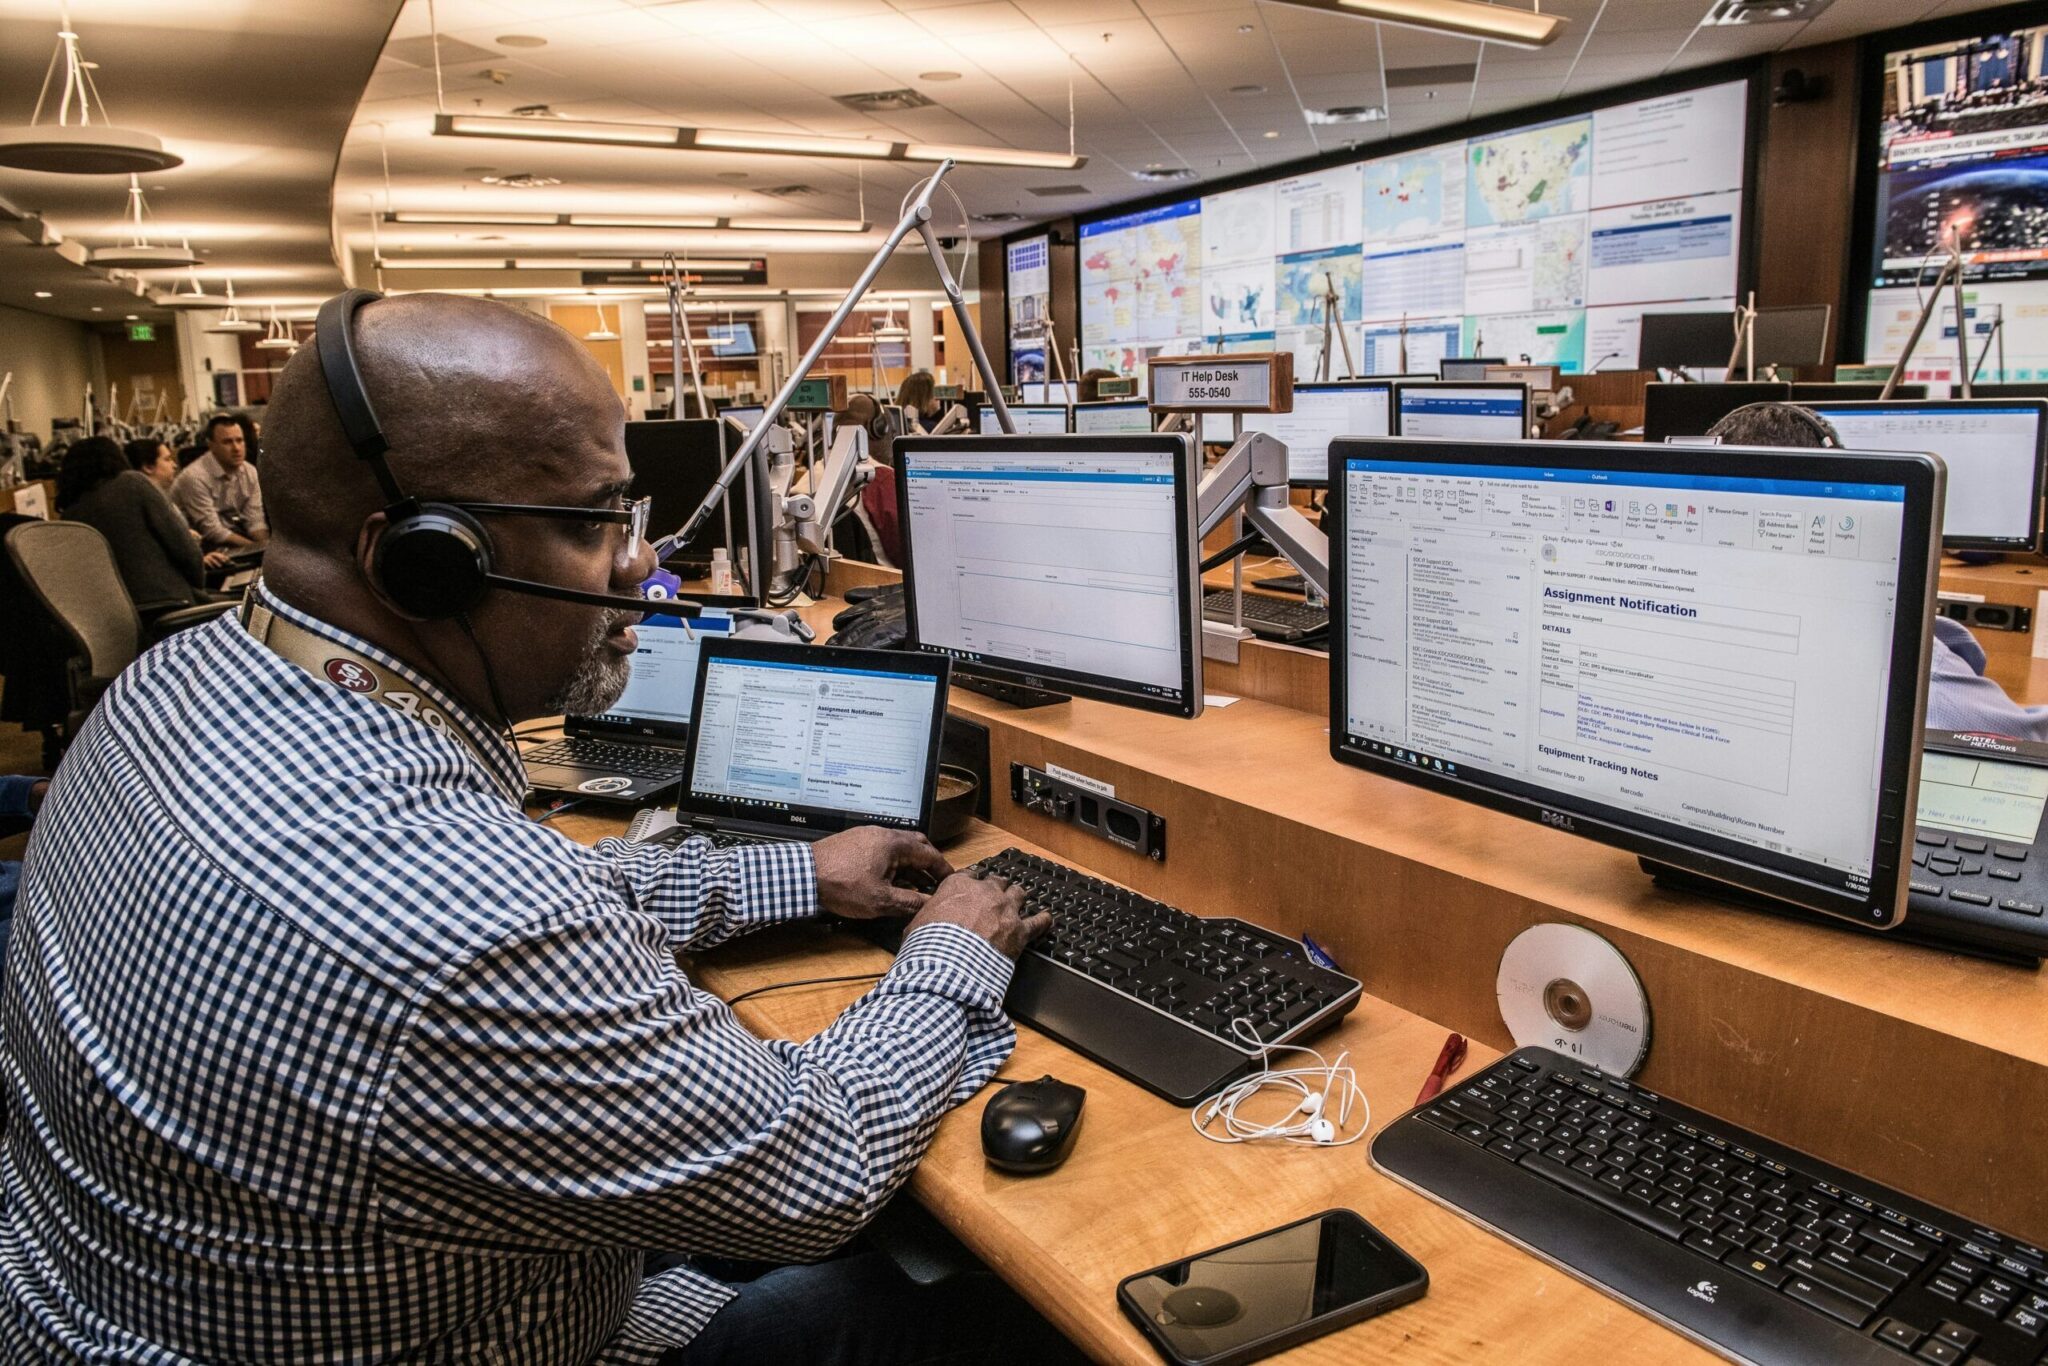
NOC vs SOC comes down to focus: a Network Operations Center keeps networks and systems running, while a Security Operations Center detects and responds to threats. Both watch the same infrastructure, often around the clock (82% of SOCs run 24/7, per SANS SOC Survey, 2025), and both still need hands onsite when the fix is physical.
For companies with many offices, that last point matters. NOC and SOC teams work remotely, so a failed switch in a branch closet or a compromised laptop at a remote site needs onsite IT network services to finish the job. This guide covers what each center does, how they differ, how they work together, and how distributed companies close the gap between remote monitoring and onsite action.
NOC stands for Network Operations Center. Pronounced “knock,” a NOC is a centralized team where a company, service provider or third party continuously monitors and manages infrastructure and technology services, as part of broader management of infrastructure and information. Telecommunication providers built the first NOCs in the late 1970s to display circuits, switches and routing status.
NOC infrastructure includes the devices an organization depends on, such as:
NOC staff watch performance, alert the right people when something degrades, and work issues until service is restored. It is a hub of people, processes and tools focused on network health and uptime.
Any business with 24-hour operations and constant connectivity needs round-the-clock monitoring. Industries that commonly rely on NOCs include:
NOCs work to protect network performance from problems such as hardware failure, circuit outages, configuration errors, traffic spikes and high user volume.
A Security Operations Center coordinates cybersecurity tools and procedures to improve a business’s ability to prevent, detect and respond to threats. Usually pronounced “sock,” it is sometimes called an ISOC (information security operations center). A SOC can be in-house or outsourced and typically monitors IT infrastructure 24/7.
A SOC analyzes information from IT assets to detect and block potential attacks. Data sources include:
Many SOC teams work at least partly remotely: 73% allow some remote work for SOC staff, according to the SANS SOC Survey, 2025. SOC specialists carry out duties such as:
Companies need SOCs to handle cyber threats at any hour and respond immediately. A good SOC also uses what it learns to tune monitoring and alerting over time. With vulnerability exploitation now the most common initial access vector (31% of breaches, per the Verizon DBIR via Help Net Security, 2026), fast detection and patch follow-through are central to the job.
A NOC focuses on availability and performance: keeping systems patched, updated and operating properly so the business meets its service level agreements. A SOC focuses on threat detection and network security. NOC technicians are trained in networking; SOC personnel specialize in security.
| Factor | NOC | SOC |
|---|---|---|
| Primary goal | Uptime and performance | Security and risk reduction |
| Typical trigger | Outage, degraded performance, failed device | Security alert, suspicious activity, threat intelligence |
| Core skills | Networking, system administration, performance management | Cybersecurity, incident response, threat intelligence |
| Key tools | Network monitoring, ticketing, configuration management | SIEM, EDR, threat intelligence platforms |
| Success measures | Availability, time to restore, SLA compliance | Time to detect, time to contain, incidents prevented |
| Weather or power outage | Leads the response | Watches for opportunistic attacks |
| Ransomware on an endpoint | Supports network isolation | Leads the response |
NOCs aim to keep networks at peak performance. A SOC’s approach centers on analysis, detection and response to security threats. Both are necessary to keep a network stable and secure.
SOC experts focus on cybersecurity, incident response and threat intelligence. NOC specialists work with network performance management, networking technologies and system administration. Some engineers cross over, but most teams hire for one discipline.
A NOC keeps IT infrastructure running smoothly, including cloud setups, endpoints and network systems. If the internet or power fails because of weather or a carrier problem, the NOC manages that interruption.
A SOC protects those same endpoints, networks and servers from cyber threats. It identifies suspect activity, analyzes it and drives remediation. It addresses ransomware and other security breaches that could compromise a network.
Both are critical to a business’s ability to operate. A NOC keeps network infrastructure running, and a SOC protects it against threats. The roles are complementary, and gaps in either one show up quickly as downtime or risk.
The cost of getting it wrong is real. In Uptime Institute’s latest survey, 57% of respondents said their most recent major outage cost more than $100,000, and the report notes that fiber and connectivity outages are rising (Uptime Institute via Business Wire, 2026).
The NOC is the control room for network infrastructure. Its experts supervise the network and handle issues that threaten availability or data through event management and monitoring. It also covers:
A SOC uses procedures, people and technology to safeguard the network. Roles typically follow tiers:
This is the question many NOC vs SOC comparisons skip. Both centers can see a problem from anywhere, but neither can reseat a cable, replace a failed switch or pull a laptop off the network at a branch office 1,200 miles away. For multi-location companies, the onsite step is often the slowest part of the response.
Common situations where a remote center needs physical hands:
Many teams solve this with remote hands or smart hands services: local technicians who follow the NOC or SOC’s instructions onsite. See our guides to remote hands for network closets and IDFs and smart hands IT services.
| Onsite coverage model | Strengths | Trade-offs |
|---|---|---|
| Staff at every site | Immediate presence, knows the site | Expensive, idle much of the time, hard to cover every office |
| Travel from headquarters | Trusted staff, consistent standards | Slow, travel costs, pulls people away from other work |
| Ask local employees to help | Fast and free | Error-prone, not trained, risky for security incidents |
| On-demand field technicians | Local coverage at many sites, pay per visit or project | Needs clear instructions, access procedures and escalation paths |
Techmate supports NOC and SOC teams at distributed companies with on-demand onsite IT support services: a network of 7,000+ vetted technicians in 450+ US cities, with a 97% resolution rate. Your NOC or SOC stays in charge of the incident while a local technician handles the physical work.
Integration: Integrating a NOC and SOC at the asset, process and system levels improves both network and security workflows. Automated data exchange between the centers saves time and frees capacity for incident response.
Communication: SOC teams rely on collaboration with stakeholders to resolve security incidents. NOC experts must also be strong communicators, though their conversations are often with fellow specialists to fix issues quickly. Shared channels and shared tickets keep both sides aligned.
When companies connect their NOC and SOC, they typically see faster remediation and response. Less duplicated data and tooling can bring operating costs down, and integration improves accountability, communication and visibility. A shared view of an incident also stops the classic problem of the NOC restoring a service the SOC was trying to keep isolated.
Different perspectives and cultures: NOC specialists focus on connectivity and uptime. They act when performance drops or an outage hits. SOC experts act on alerts, attack analysis and incident response. While the NOC examines packet flows, the SOC looks at how a threat entered and spread. Those priorities can conflict during an incident.
Mitigating risk: Establishing shared workflows between the NOC and SOC is crucial. Clear goals, defined handoffs and the right tools reduce the challenges of integration.
Staffing and coverage: Round-the-clock coverage requires shifts, and skilled analysts are hard to hire. Many organizations outsource one or both centers, or use a co-managed model.
Distributed sites: Remote centers see everything but can touch nothing. Without a plan for onsite work, every physical issue becomes an escalation scramble.
| Model | Good fit when | Watch for |
|---|---|---|
| In-house NOC and SOC | Large IT team, strict regulatory needs, budget for 24/7 staffing | Hiring, shift coverage and burnout |
| Outsourced NOC and SOC | Lean internal team that needs 24/7 coverage quickly | Handoffs, visibility and who owns remediation |
| Hybrid or co-managed | Internal team owns strategy, provider covers nights or specialties | Clear lines of responsibility in every runbook |
| Any model plus onsite field support | Many offices, branches or remote sites | Site documentation and access procedures |
For more on shared models, see co-managed IT services.
NOC and SOC are centralized teams that monitor and manage IT environments, but with different goals. The NOC focuses on network and system performance and uptime. The SOC focuses on detecting and responding to cyber threats. Together, they form a strong foundation for secure, reliable operations and support a broader IT strategy.
No. Both monitor networks, but their roles are different. The NOC is concerned with network operations and performance, while the SOC oversees security and information assets. They often watch the same devices and alerts, so working together helps them manage risk without stepping on each other during an incident.
NOC engineers keep IT infrastructure available so the business can operate: they troubleshoot outages, manage configurations and handle maintenance. SOC engineers protect that infrastructure from threats: they investigate alerts, contain incidents and improve detections. Both benefit from understanding the other’s work.
In many cases, yes, or at least closely integrated. Both depend on the same infrastructure and often the same data. Integration reduces duplicate spending, shares knowledge across teams and speeds up response. Smaller organizations often get there through a co-managed or outsourced model rather than building two separate centers.
They diagnose remotely, then need someone onsite for physical tasks like swapping hardware, console access or isolating a device. Options include local staff, travel from headquarters or on-demand field technicians who follow the NOC or SOC’s runbook while staying on a live bridge with the engineer.
A small company rarely needs its own dedicated centers, but it still needs the functions: monitoring for outages and monitoring for threats. Many smaller organizations get both through a managed or co-managed provider, then add onsite support for the physical work at their offices.
Whatever your NOC vs SOC setup, both teams can see problems anywhere, but distributed companies also need a fast way to act on them at every site. Start with a free 30-minute IT support audit to map where your onsite coverage has gaps and how to fill them.